PCI DSS Compliance in the UAE
Take card payments in the UAE? PCI DSS applies to you — and it is one of the few standards that explicitly requires penetration testing. Here is what that means in practice.
Take card payments in the UAE? PCI DSS applies to you — and it is one of the few standards that explicitly requires penetration testing. Here is what that means in practice.
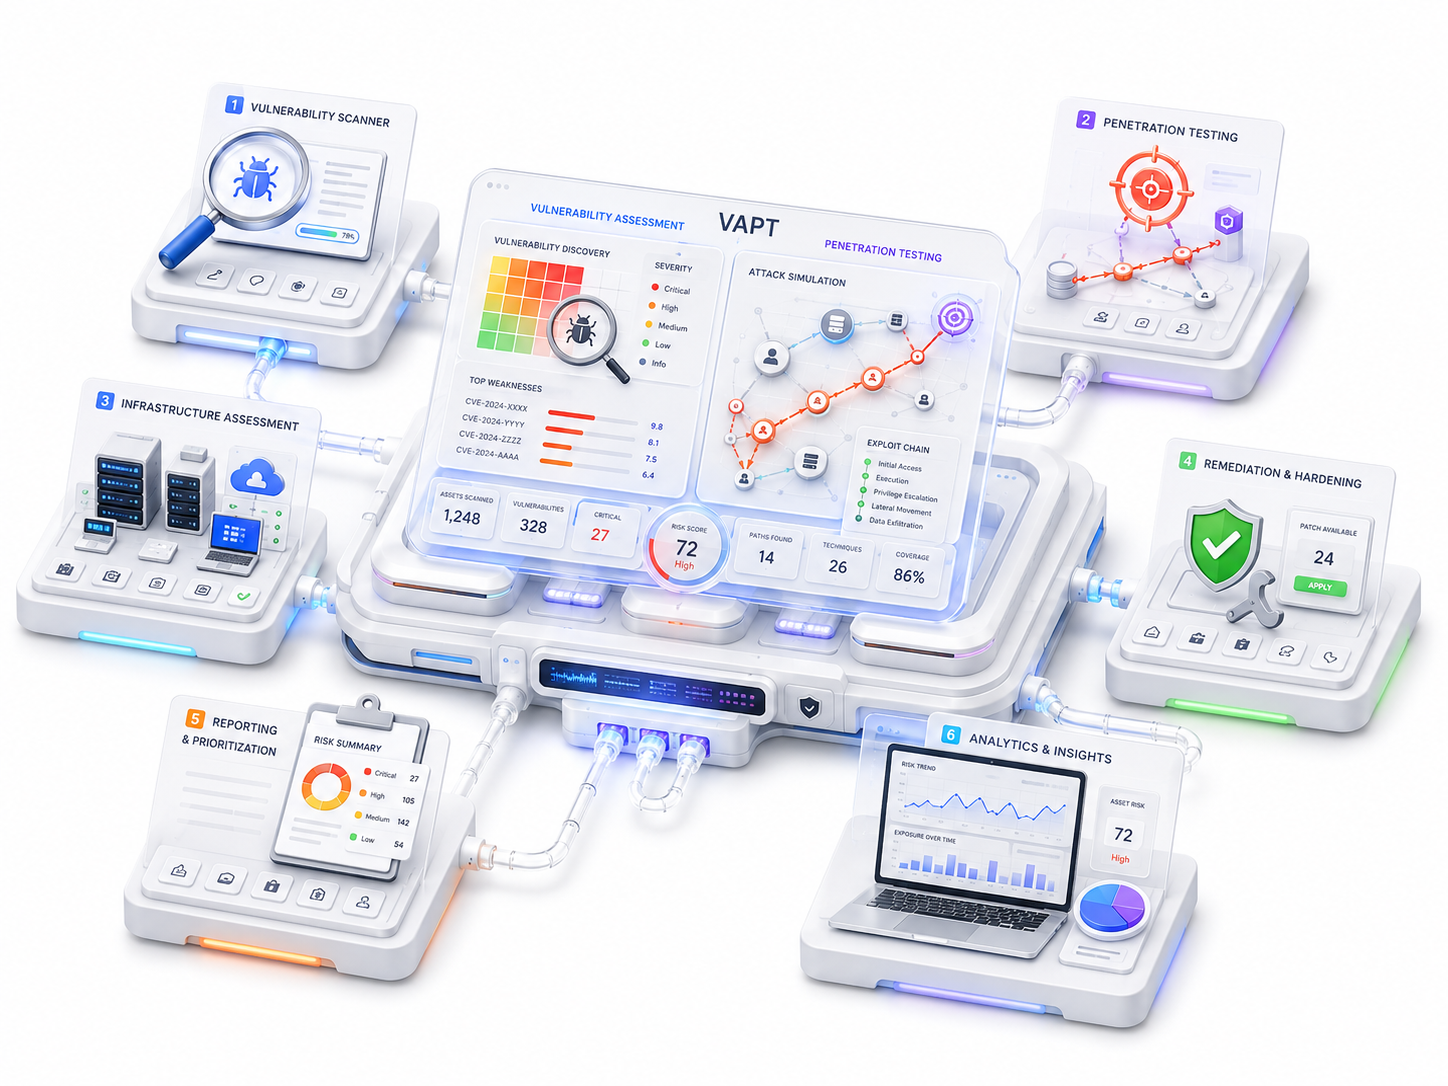
PCI DSS — the Payment Card Industry Data Security Standard — applies to every organisation that stores, processes or transmits cardholder data: e-commerce, retail, hospitality, fintech. It is enforced through your acquiring bank, and in the UAE acquirers are increasingly strict about evidence. The standard is maintained by the PCI Security Standards Council.
Requirement 11 mandates regular security testing: internal and external penetration testing at least annually and after significant changes, plus segmentation testing if you rely on network segmentation to reduce scope. This is one of the few frameworks where a pentest is not “best practice” but a written requirement.
Your PCI DSS testing checklist:
The cheapest cardholder data environment is a small one. Tokenisation, hosted payment pages and real network segmentation shrink what needs testing — we routinely help clients cut their PCI testing scope before quoting, which usually saves more than the test costs.
Yes — Requirement 11 mandates internal and external penetration testing at least annually and after significant changes, plus segmentation testing where applicable.
Your acquiring bank enforces it contractually; non-compliance risks fines and losing the ability to process cards.
A test proving that your cardholder data environment is genuinely isolated from the rest of your network, so your PCI scope stays small.
Shrink the cardholder data environment: tokenisation, hosted payment pages and real segmentation reduce what must be tested and audited.
Next step
Book a free 30-minute strategy call. You get clarity on scope, approach and a fixed price — no obligations.